FlareOn 8 - 0x1 - Credchecker
A walkthrough of the Credchecker challenge from FlareOn 8, reversing the client-side credential-validation logic.
Challenge
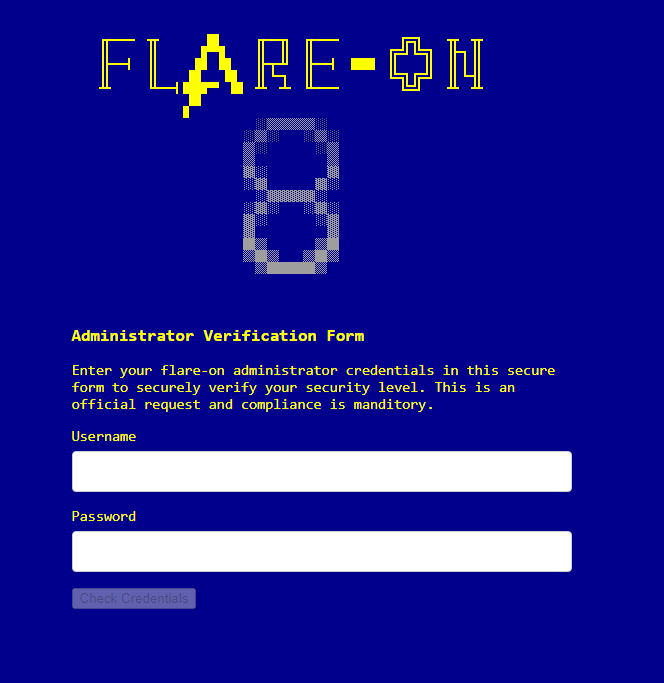
There is an HTML page showing a login form in which you have to put some credentials:
 Of course, you don’t have the credentials. If you put anything wrong, it popups an error:
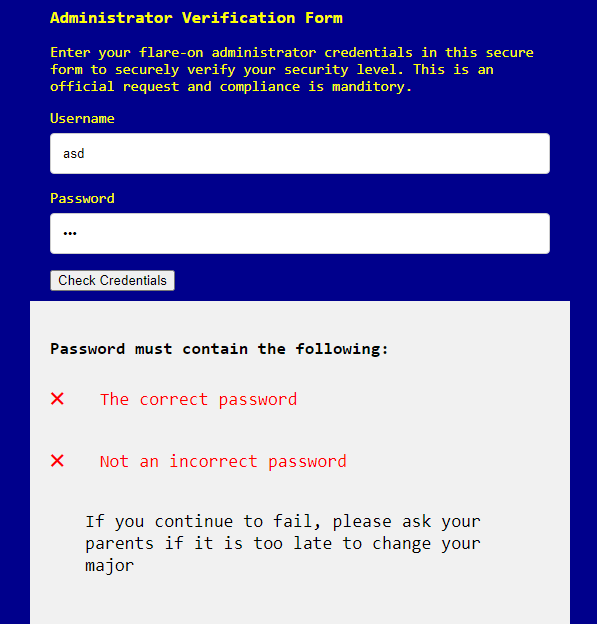
Goal: find the right combination of the credentials to solve the challenge.
Solution
Easy challenges anyone? The directory contains only an HTML page, so the code is hidden inside the source. It takes a second to quickly find the logic that does the check:
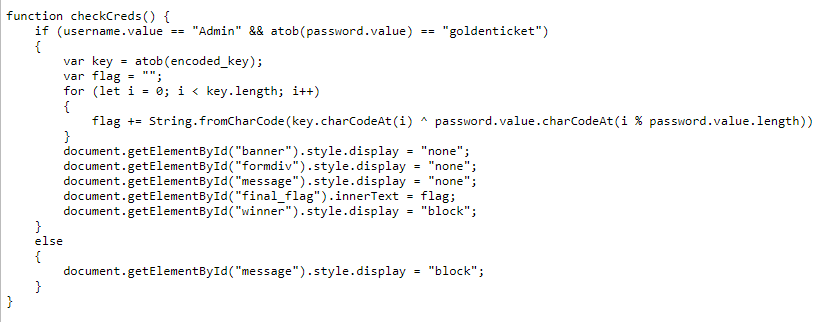 For the user, it just needs to be “Admin”. For the password particularly, the line
atob(password.value) == "goldenticket" invokes a particular atob() function that transforms the input password, and if it’s equal to goldenticket passes the check and shows the flag. From JS docs:
The
atob()method decodes a base-64 encoded string.
So we calculate the base64 encoding of goldenticket:
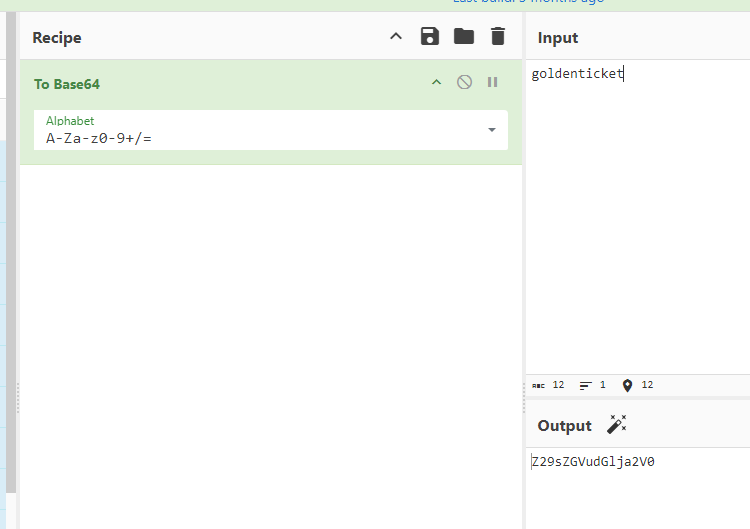 and then we input
Z29sZGVudGlja2V0 inside the form: